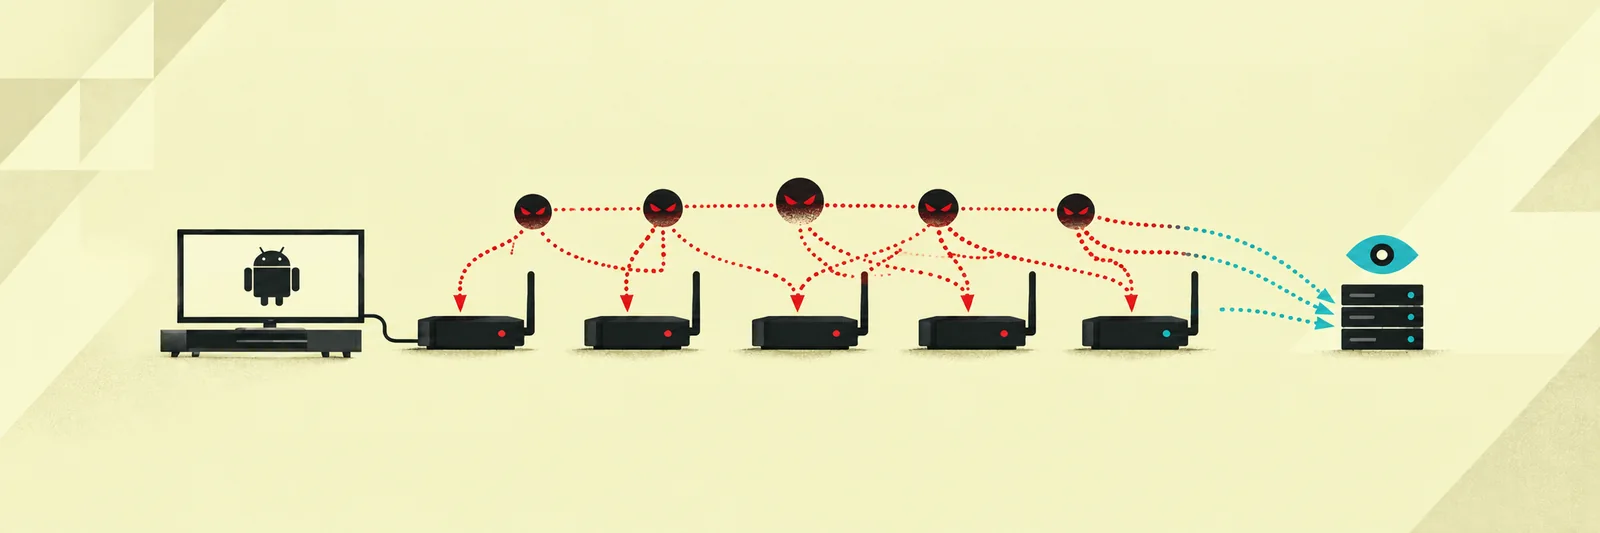
Into the Vo1d: Hunting a Botnet Hidden in TV Boxes
A BSides Lisbon talk connecting malware analysis, DNS intelligence, and sinkhole telemetry in an Android TV botnet investigation.
A BSides Lisbon talk connecting malware analysis, DNS intelligence, and sinkhole telemetry in an Android TV botnet investigation.
Tracing changes in PrivateLoader protocols and string obfuscation, with YARA and Suricata detection.
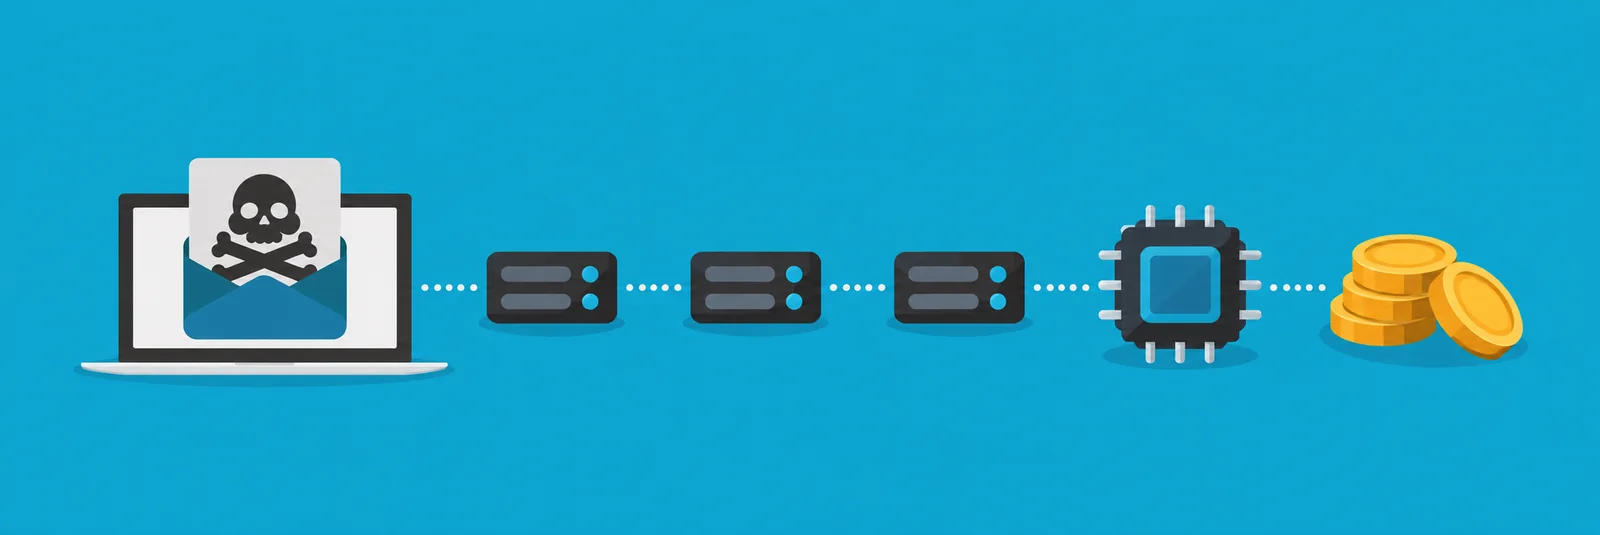
Investigating the proxying, spam, and cryptocurrency-mining activity of the modular Tofsee botnet.
A Colibri Loader unpacking walkthrough covering anti-analysis techniques, string decryption, and YARA detection.
Building a PrivateLoader string decryptor and YARA rule from a stack-based XOR pattern.