Amadey and StealC: Malware-as-a-Service Unavailable
C2 mapping, malware emulation, and infection telemetry supporting the Amadey and StealC disruption.
C2 mapping, malware emulation, and infection telemetry supporting the Amadey and StealC disruption.
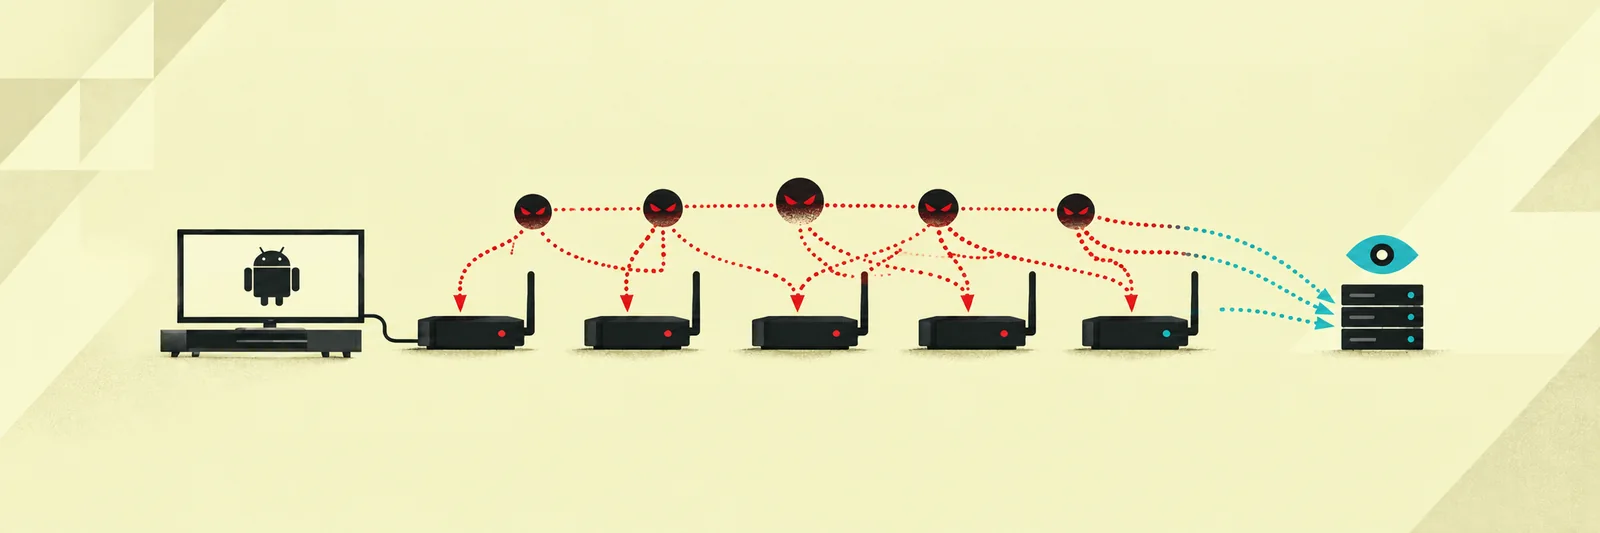
A BSides Lisbon talk connecting malware analysis, DNS intelligence, and sinkhole telemetry in an Android TV botnet investigation.
Tracing changes in PrivateLoader protocols and string obfuscation, with YARA and Suricata detection.
A Colibri Loader unpacking walkthrough covering anti-analysis techniques, string decryption, and YARA detection.
Tracking PrivateLoader delivery chains and identifying 30 malware families in the collected payloads.
Building a PrivateLoader string decryptor and YARA rule from a stack-based XOR pattern.