Amadey and StealC: Malware-as-a-Service Unavailable
C2 mapping, malware emulation, and infection telemetry supporting the Amadey and StealC disruption.
Malware analysis · C2 tracking · DetectionSenior Threat Researcher
I reverse engineer malware, track botnet infrastructure, and develop detection and research tools.
Lisbon, Portugal · Malware analysis & botnet tracking
C2 mapping, malware emulation, and infection telemetry supporting the Amadey and StealC disruption.
Malware analysis · C2 tracking · Detection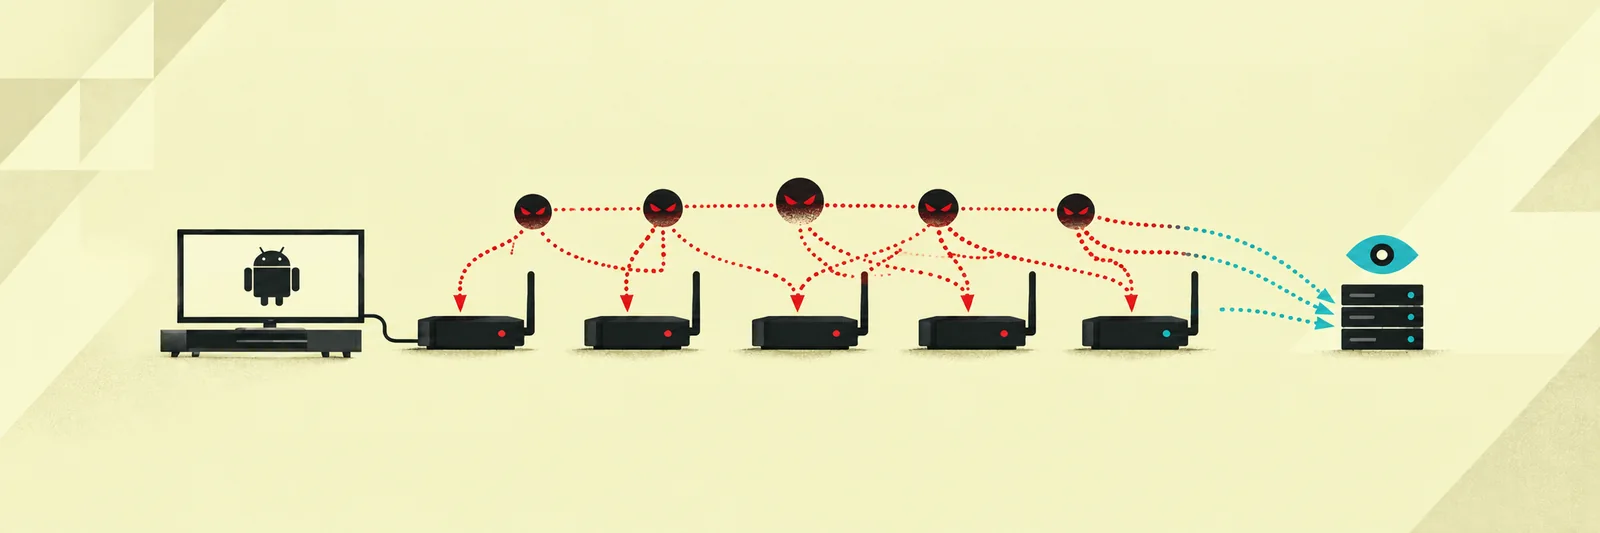
A BSides Lisbon talk connecting malware analysis, DNS intelligence, and sinkhole telemetry in an Android TV botnet investigation.
IoT malware · Threat hunting · Technical speaking
An investigation of Telegram bot exfiltration, infostealer log formats, and the visibility those records provide.
Exfiltration analysis · Data processing · Threat intelligenceFor research conversations, collaboration, or professional opportunities:
[email protected]